
 Vaultic
Webhooks & audit log
Workspace-level outbound webhooks, and the write-event audit trail.
Webhooks
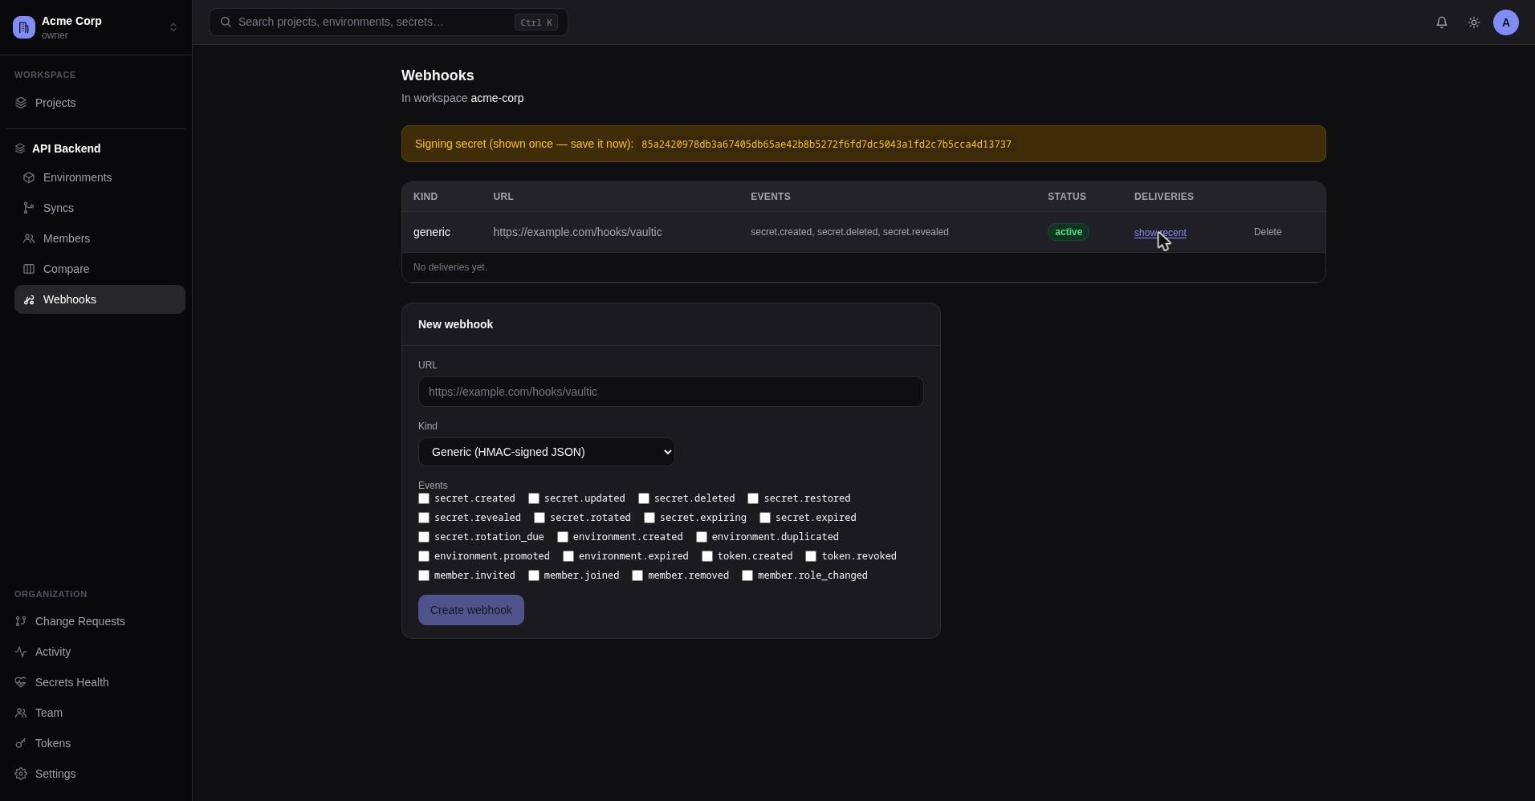
Workspace-level outbound webhooks — generic HMAC-signed JSON, or a Slack incoming webhook. The table shows kind, URL, subscribed events, active/disabled status, an expandable recent-deliveries list (timestamp, event, ok/failed with error or status code), and a delete action.
Creating one takes a URL, a kind, and a checkbox list of event types to subscribe to. New generic (non-Slack) webhooks show a one-time signing-secret banner right after creation.
See CLI: sharing & webhooks for the full event catalog and the CLI equivalent.
Activity
The workspace-wide audit log: When / Actor / Action / Target key / Project / Source (web, API, or token) for every write event. Only write events are logged here — masked list/get reads are not.
Supports date-range filters (From/To) and an Export button that downloads the filtered log as CSV or JSON.
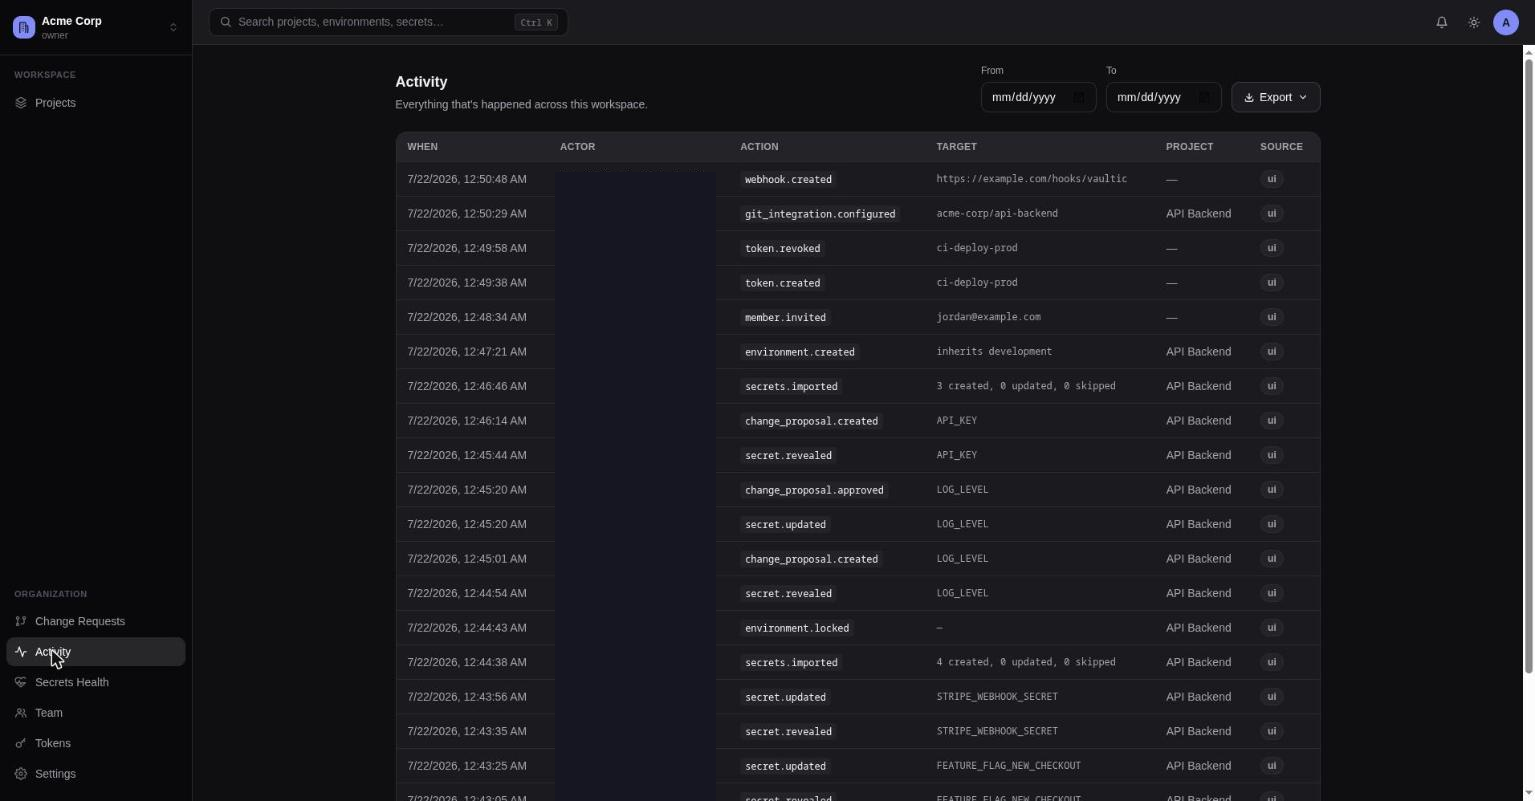
Every reveal and every export is its own distinct audit event (secret.revealed,
environment.exported) — separate from secret.created/updated/list — so revealing or
exporting a value is always individually traceable.